

-
Risk Culture
-
Risk Management Objectives
-
Risk Appetite
-
Overview of the Risk Management Process
-
Risk Assessment and Treatment
-
Monitoring and Review
-
Consultation and Reporting
-
Overview of ERM Integration
-
ESG Risk Integration and Climate Resilience
-
Business Resilience and Continuity Management
The Group embraces a risk-aware culture and believes that an ingrained risk culture is the key to effective risk management, while training is a useful tool to promote and engage management and employees in ERM implementation. The Group promotes the risk culture with the following key themes:
- Effective ERM is beyond processes and forms – it is a change of culture in terms of mindset and behaviour.
- ERM is not a standalone programme – it should be tailored and embedded in the Group’s business processes.
- ERM deals with both risks and opportunities – appropriate risk-based treatments can control risks and even seize further opportunities of value creation.
The Group's ERM Framework aims to enhance the ability to achieve its vision and mission, and fulfil its five core values. In support of this, the Group has established a robust ERM framework with the following risk management objectives:
- To fulfil our commitment to integrity, ethics and compliance as an integral part of our corporate governance
- To build agility and resilience amid uncertainty in dynamic business environment
- To facilitate risk-informed decisions and align the Group’s objectives, strategy and operations with the risk appetite
- To strengthen our capacity for seizing opportunities and safeguarding our assets to support our sustainable growth and create shared value
Risk appetite is defined to establish the extent and nature of risks the Group is willing to take in achieving our vision and mission. The Group’s risk appetite statement is disseminated across the Group and incorporated into our risk assessment criteria in order to align with our business objectives, core values, strategy, as well as risk management activities. The risk appetite statement is reviewed by the Board periodically to keep abreast of the ever-changing business environment and the latest development of the Group. The Group’s risk appetite is as follows:
- The Group upholds the highest standards of integrity, compliance, and ethics and has no tolerance for any material breaches of laws and regulations.
- The Group has no compromise on any threats which may significantly impact the health and safety of our people.
- The Group does not expose itself to any potential material damage to its reputation or brand.
- The Group proactively reduces its environmental footprint by embedding environmental considerations across its value chain, advancing its net-zero pathway, and avoiding activities that may significantly harm the environment.
- The Group respects human rights and promotes inclusive and equitable practices across its operations and supply chain. It seeks to create positive societal impact through responsible charitable partnerships, while refraining from activities that may cause significant harm to its people, stakeholders, or communities.
- The Group endeavours to minimize any business interruptions and significant operational impacts to business continuity. In addition, the Group remains vigilant to operational risks arising from climate change and continues to strengthen its climate adaptation measures to enhance operational resilience.
- The Group is prudent in making decisions that may threaten its long-term financial viability and liquidity to meet its financial commitments.
- The Group balances risks and opportunities whilst implementing strategies to minimize failure in business decisions, reduce shortfalls in achieving its ESG commitments and net zero pathway, and optimize the Group’s long-term value.
The overall risk management process is overseen by the Board. With the emphasis on value creation and protection, the Group adopts the Three Lines Model as its risk governance structure. The model clearly defines the responsibilities for enhancing collaboration and communication among different roles, which facilitates alignment of risk management activities and provides assurance to the Board.
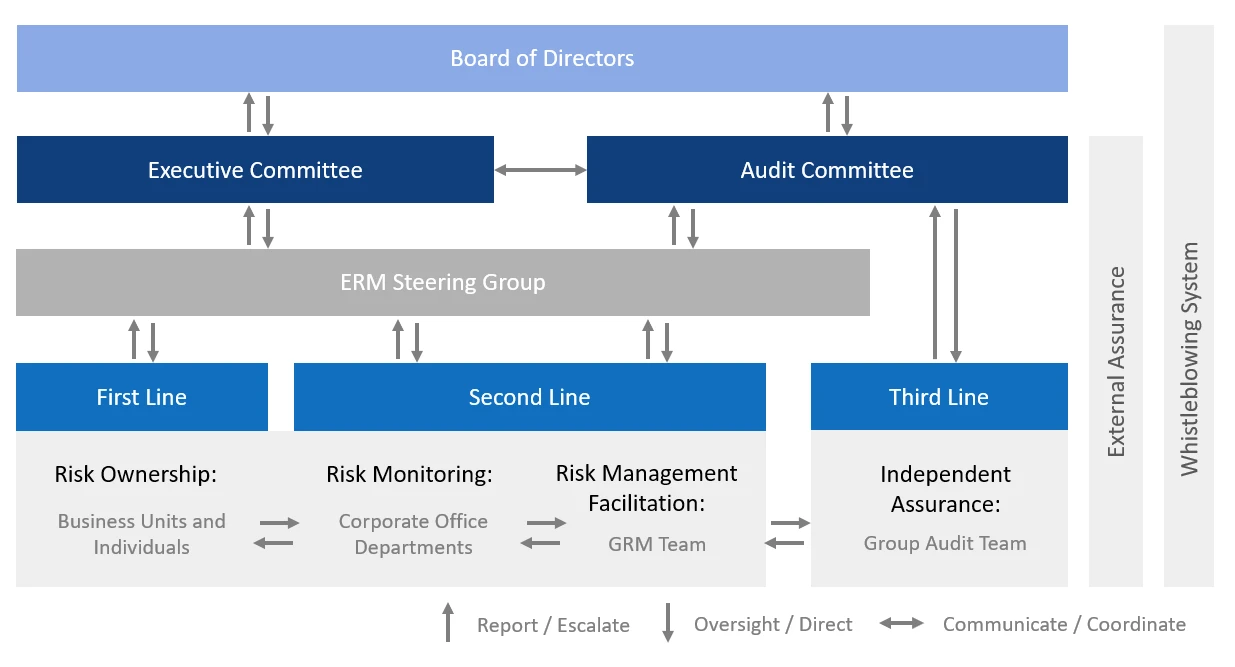
- Hold the ultimate responsibility for the Group’s risk management and internal control systems
- Ensure the appropriateness, adequacy and effectiveness of the Group’s risk management and internal control systems through the Audit Committee’s reviews
- Determine and review the risk appetite to ensure its continual alignment with the Group’s core values, strategic objectives, business context, risk capacity and the evolving risk landscape
- Empower and delegate the oversight responsibility of risk management and internal control systems to the Audit Committee
- Provide independent oversight on the risk management and internal control systems and review their appropriateness, adequacy and effectiveness
- Review the risk profile of the Group and advise the Board on the current and potential risk exposures and their corresponding risk treatment plans
- Determine and allocate sufficient resources to effectively implement the ERM system
- Review and prioritize the Group’s key risks and endorse the risk treatment plans
- Ascertain the effectiveness of the risk management and internal control systems
- Lead and supervise the implementation of the Group’s risk management and internal control systems
- Advise the Audit Committee and the Executive Committee on all ERM-related matters
- Improve risk awareness and promote risk-aware culture across the Group
- Act as risk owners to perform risk assessments to identify, analyze, and evaluate risks in daily operations and in areas of accountability
- Design, implement and evaluate risk treatment plans and report in the Risk Register on a regular basis
- Maintain a repository of material controls and conduct periodic self-assessment on the effectiveness of internal control system
- Establish appropriate governance bodies to provide effective oversight of material risk exposures, taking into account the organization’s unique business nature, risk profile and regulatory environment, and ensuring such risks are managed within the established risk appetite
- Act as risk owners and perform ERM responsibilities for respective departments
- Remain current with best practices and provide recommendations to the ERM Steering Group
- Assist management in the design and development of ERM processes and risk mitigation plans
- Facilitate the risk management process, including the identification and monitoring of the known and emerging risks, aggregation and prioritization of the key risks identified by the Group as well as reporting to senior management and committees
- Promote risk-aware culture across the Group
- Monitor the KRIs and review the implementation of risk mitigation plans
- Evaluate the adequacy, appropriateness, effectiveness and efficiency of the risk management and internal control systems
- Consider the key and emerging risks and key control processes upon formulating the annual audit plan and planning for each audit
- Perform risk-based validation of the risk treatment plans
- Provide independent observations and recommendations on the Group’s processes and controls over financial reporting
- Provide independent assessment of the process and procedure of the ERM system in accordance with relevant regulatory requirements or Risk Management Standard (e.g. ISO 31000:2018 Risk Management), depending on the scope of the assessment
- Advise on best practice and/or assure compliance, if necessary
- Execute regulatory oversight on relevant entities, areas or activities
- Provide an independent and confidential channel for stakeholders to directly report to Group Audit team for any serious concerns about suspected or actual fraud, corruption, breach, malpractice, misconduct or irregularity of the Group and/or its staff member. Please refer to the Corporate Governance Report of this annual report for details
Risk management process starts from the establishment of context, by taking into consideration of the external environment and megatrends, as well as risk universe of the Group. Risks are then identified, analyzed, evaluated and treated with measures. With constant review, monitoring, reporting and consultation, the risk management process integrates with various business processes and activities in optimizing the risk and return.
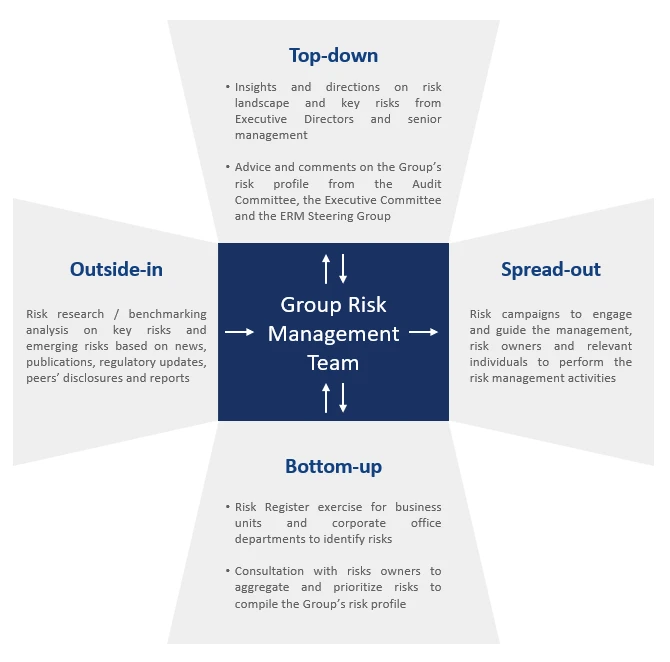
To facilitate a comprehensive and robust risk management process, top-down and bottom-up approaches are employed to gather risk insights as well as to monitor and manage risks from the perspectives of both sides, together with “ERM Policy” and “ERM Procedure” to provide proper guidance. Also, interactive communication between the risk owners and the GRM Team is in place to enable both parties to keep abreast of risk updates.
Risk Management Process
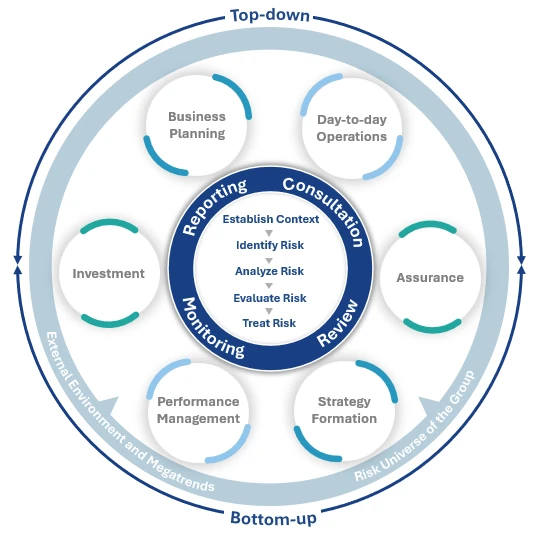
1. Establishment of Context
The Group defines the internal and external contexts (e.g. corporate objectives, core values, organizational structure, stakeholders, business segments, operating regions, regulatory environment) as well as the parameters for risk assessment criteria.
2. Risk Identification
The Group adopts both top-down and bottom-up approaches, complemented with outside-in and spread-out mechanisms to facilitate a comprehensive risk identification process.
3. Risk Analysis
The Group adopts a two-phased methodology where business units and corporate office departments need to conduct a preliminary risk assessment to sort out key risks for undergoing comprehensive risk analysis, and a diverse spectrum of risk assessment criteria is applied throughout the process covering likelihood, impact, risk velocity, forecast risk movement, inherent risk level and residual risk level.
4. Risk Evaluation
The risk analysis results are compared with the risk appetite and tolerance level. This allows management to determine the risk response strategy for each risk and prioritize risk treatment plans.
5. Risk Treatment
Risk treatment plans for implementing risk mitigation measures are developed by respective business units and corporate office departments, based on the priority and nature of risks.
Continual tracking, review and validation of the implementation of our ERM framework have been in place to monitor various risks, change in risk exposure, their residual risk levels, as well as to ensure and increase the effectiveness and quality of ERM framework and outcomes.
| Top-Down Engagement (Annually) |
The GRM team conducts in-depth risk discussion on emerging political, economic, social, technological, legal and environmental (“PESTLE”) trends in our business context with the senior management of the Group and its business units to obtain their insights on the risk landscape faced by the Group. |
| Bottom-up Risk Register Review (Semi-annually) |
Business units and corporate office departments perform review of the risk assessment and risk treatment plans, and submit Risk Registers to the GRM team for consolidation into the aggregated risk profile of the Group. |
| Key Risk Indicator Monitoring (Quarterly reporting, with immediate notification of any exceedance upon detection) |
The Group adopts a two-tier KRI structure comprising Principle KRIs and Agile KRIs to monitor changes in risk exposure of key risks, where Principle KRIs are standardized indicators applied across business units to provide consistent oversight on potential risk appetite exceedance, while Agile KRIs are customized indicators designed to reflect the unique risk characteristics of different business units, supporting more dynamic monitoring of changing risk profiles. If there is any KRI value exceeding the pre-defined threshold, risk alerts to management will be mandated so that they can timely administer corresponding responses, and proper reporting to Executive Directors will be made. The GRM team also monitors the KRIs and corresponding follow-up actions for any exceedance. |
| Risk Treatment Validation (Annually) |
The GRM team reviews the implementation of risk treatment measures stated in the Risk Register or KRI Report. The Group Audit team also performs risk-based validation to test risk treatment measures of key risks during the internal audit process. |
| Material Control Repository and Integrated Internal Control Self-Assessment (Semi-annually) |
Business units and corporate office departments review the repository for key business processes and associated material controls and conduct Integrated Internal Control Self-Assessment to evaluate and ascertain the effectiveness of their risk management and internal control systems, with reference to the COSO framework. |
| Early Flagging Mechanism (On-going) |
An early risk flagging mechanism is applied across the Group, to proactively identify and assess emerging risks and risks with high velocity, such as quality, health and safety, disaster and media events. When a potential risk is perceived with significant impact, the risk should be flagged and reported to the relevant line manager and risk oversight parties. |
| Whistleblowing Mechanism (On-going) |
The Group has established a Whistleblowing Policy and provided reporting channels for internal and external stakeholders. Whistleblowing cases are reported to the Executive Committee and Audit Committee. |
| Independent Review of ERM System (Annually) |
Independent review of the ERM system’s processes and procedures is performed annually by an independent qualified external assessor or the Group Audit team. In FY2026, the Group has engaged SGS Hong Kong Limited (“SGS”) to assess its ERM implementation in accordance with ISO 31000:2018 Risk Management — Guidelines. |
Regular reporting, regarding identified risks and the status of risk management activities, is provided to management, the ERM Steering Group, the Executive Committee, the Audit Committee and the ESG Committee to facilitate the risk management process and decision-making. The ERM Steering Group Meeting is held every half year to discuss key risk matters and updates.
The Group operates and invests in a diversified portfolio of businesses predominantly in Hong Kong and the Chinese Mainland, including financial services, toll roads, logistics, construction, and facilities management.
Through the comprehensive risk management process described in the previous section, the Group has identified major risks which may affect the achievement of its business objectives. However, risks evolve through interactions among various dynamic forces and factors in the business environment. Certain risks that are not currently significant may emerge as key risks in the future, while other risks may not yet have been identified. Accordingly, our risk portfolio is regularly reviewed and updated to react and respond to the changing risk landscape.
Overall Risk Trend and Emerging Risk Drivers
The Group’s risk environment in FY2026 continues to be influenced by the pace of economic recovery in Hong Kong and the Chinese Mainland, geopolitical tensions, trade policy uncertainty and an increasingly demanding regulatory landscape. Although interest rate volatility has moderated and inflation remains relatively contained, economic growth across the region remains uneven. Hong Kong’s GDP growth is forecast at 2.5%–3.5% in 2026, while the Chinese Mainland is expected to maintain moderate growth amid ongoing economic restructuring.
While these developments may affect consumer spending, investment decisions and financing conditions, the Group remains resilient, supported by a strong balance sheet, healthy liquidity position and prudent financial management practices. Existing liquidity resources and funding capacity are considered adequate to support business operations and strategic initiatives under both normal and stressed conditions. Notwithstanding the external uncertainties, the Group’s overall risk profile remains within its risk appetite.
Technology transformation remains a strategic priority for enhancing the Group’s competitive position. Advances in artificial intelligence, automation and digital solutions present significant opportunities to improve operational efficiency, customer engagement and decision-making capabilities. Across the Group, various business units are accelerating the adoption of emerging technologies, with investments subject to pilot implementation and ongoing evaluation to ensure they are supported by demonstrable business value, appropriate use cases and prudent cost-benefit considerations prior to wider deployment. For example, the insurance business utilizes digital platforms, data analytics and AI-enabled solutions to enhance customer experience, streamline operational processes and strengthen distribution effectiveness. Meanwhile, the construction business is expanding the use of smart site technologies and construction robotics to improve quality, productivity, safety and cost control, while fostering a more modern and technology-enabled working environment that supports attraction and retention of next-generation talents.
As reliance on technology grows, the Group faces heightened risks relating to cybersecurity threats, data privacy and AI governance. The Group will reinforce technology risk management, cybersecurity capabilities and governance frameworks to ensure these transformation initiatives are implemented in a secure, resilient and responsible manner. In parallel, certain business units have developed dedicated AI governance frameworks to support the responsible adoption of AI, with a focus on accountability, risk assessment, human oversight, continuous validation and ongoing training. The Group also promotes employee awareness and capability building through training programmes designed to encourage the effective use of emerging technologies, such as generative AI, while reinforcing the importance of cybersecurity, data protection, and ethical and compliance considerations. In addition, the Group’s expansion into digital infrastructure may introduce new technology, operational and regulatory considerations, which will continue to be incorporated into the Group’s risk assessment and monitoring processes.
Climate-related risks continue to grow in significance. The increasing frequency and severity of extreme weather events, evolving transition requirements associated with decarbonization initiatives and expanding ESG disclosure expectations may impact business operations, asset values, project delivery and stakeholder expectations. The Group continues to enhance its climate risk management capabilities through climate scenario analysis, business continuity planning, infrastructure resilience measures and sustainability initiatives under its ESG strategic priorities.
Looking ahead, the Group will maintain a vigilant and forward-looking approach towards emerging risks and opportunities. By strengthening risk awareness, enhancing resilience and promoting innovation, the Group remains well positioned to navigate uncertainties and support sustainable value creation for its stakeholders. Please refer to the following table for the major risks identified by the Group and the corresponding response measures. This is neither intended to be exhaustive nor comprehensive.


Macroeconomic Risk
Risk Description
Global economic uncertainties and slow recovery affecting business growth and financial performance
Risk Trend
Mitigation Measures
- Evaluate the potential impacts from the economy by analyzing the financial performance and monitoring business and economic data continuously
- Optimize business / customer portfolios to reduce impact from economic fluctuation and diversify the risk
- Identify opportunities for business collaboration and partnership to leverage the synergies within the CTF Group's diverse business network
- Perform sensitivity assessment on potential impacts in relation to economic conditions leading to lower valuation
- Explore new business opportunities or new sources of income for new growth drivers
- Closely monitor movement of foreign currency exchange rates and consider to arrange currency hedging contracts should the need arises
Competition Risk 
Risk Description
Intense competition arising from existing competitors and/or new entrants to the market regarding the industries the Group is operating
Associated ESG Issue:
Innovation and Digitalization
Risk Trend
Mitigation Measures
- Expand and maintain the market share by effective customer incentive programmes and sound customer relationship management
- Conduct market and competitor analysis to evaluate our competitive position and formulate corresponding strategic plans
- Utilize technology to optimize customer experience and operational efficiency
- Pursue advanced qualifications and industrial-recognized accreditations to strengthen our technical capabilities and competitive edge
- Leverage CTF Group synergies to strengthen competitive advantage
Government Policy and Intervention Risk
Risk Description
Imposition of government policies, intervention, laws or regulations, exposing the Group to legal or regulatory liabilities, business disruption, reputational damage and/or financial loss
Risk Trend
Mitigation Measures
- Closely monitor changes in applicable government policies, laws and regulations, and formulate appropriate responsive strategies and plans
- Provide updates and/or training to staff to cope with the new government policies and practices
- Proactively communicate with external parties (e.g. the relevant council or association) to understand the changes and express opinions collectively
- Partner with consultants, scholars and universities to get the advice on adapting changes in government policy
Geopolitical risk
Risk Description
Conflicts between nations, political issues towards individual business, political instability and etc., impacting the Group’s ability to sustain its profitability
Risk Trend
Mitigation Measures
- Pay close attention to the latest development of geopolitical issues and assess impact of the issues
- Seek professional advice on any regulatory changes due to political factors such as sanctions
- Widen investment universe by considering investors and assets from different background (e.g. industry, nationality, source of funds, etc.)
- Delay spending of capital expenditure in concerned regions based on the situation
- Diversify the impact of geopolitical issues by investing in business opportunities across different regions and markets
Cybersecurity Risk
Risk Description
Cybersecurity issues compromising data integrity, confidentiality and system availability, which may lead to adverse impacts on reputation, financial conditions, and operational performance
Associated ESG Issue:
Cybersecurity and Information Security
Risk Trend
Mitigation Measures
- Establish comprehensive information security protection with well-defined policies and security controls such as authorization and authentication mechanisms, firewalls with advanced threat controls, network immune system, proper access controls
- Provide periodic training and conduct phishing drill exercises to promote cybersecurity awareness
- Purchase cybersecurity insurance to cover losses arising from cyber incidents or data loss events
- Engage information security specialists to assess cybersecurity vulnerabilities and controls
- Ensure compliance with regulations and standards. Regularly update security protocols to maintain high standards and address emerging threats
Project Management Risk
Risk Description
The risk of improper planning, execution, monitoring or control of a major project, impacting the Group’s achievement of strategic goals and financial performance
Risk Trend
Mitigation Measures
- Conduct comprehensive project planning, risk assessments, and resource allocation to support effective project delivery
- Monitor project progress, costs, quality, safety, and operational performance through regular meetings, site inspections, and management reviews
- Implement early warning, change management, reporting, and escalation mechanisms to promptly address project issues, delays, and cost overruns
- Strengthen project management capabilities through staff training, talent development, retention initiatives, and adequate manpower planning
- Enhance supply chain and subcontractor management through supplier diversification, performance evaluations, strategic backup arrangements, and timely payment practices
Quality, Health and Safety Risk
Risk Description
Sub-standard or unsafe product, service or business activities impacting the achievement of the Group’s quality, health and safety goals
Associated ESG Issue:
Responsible Product and Services, Health and Safety
Risk Trend
Mitigation Measures
- Implement quality assurance programme and review performance data to ensure consistent performance and service quality
- Develop procedures and guidelines to set standards for quality, health and safety and deliver regular training to employees to enhance their safety awareness and service performance
- Arrange customer satisfaction surveys to collect voice of the customers
- Perform evaluation of each accident or complaint to identify improvement areas and take follow-up actions
- Establish designated committee to enhance the governance on complaint handling
- Establish comprehensive safety management system and conduct regular safety inspection and audit
- Utilize advanced technologies to improve quality, health, and safety standards
Talent Attraction and Retention Risk
Risk Description
Failure to attract and/or retain qualified staff to support operations impacting the achievement of business objectives
Associated ESG Issue:
Talent Attraction, Retention and Development
Risk Trend
Mitigation Measures
- Review the existing remuneration packages and compare with industry benchmark periodically
- Provide development and training programmes to improve staff’s competency and promote career progression
- Foster the caring culture by offering a variety of wellness programmes, employee engagement activities and channels to enhance cohesion between the Group and its employees, and to obtain voice of employees and address their needs
- Expand the channels for reaching talent and promote the Group’s employer branding to increase the competitiveness in the talent market
- Leverage automation and robotic technologies to mitigate ageing workforce issues, while cultivating an innovation-driven culture to attract and retain next generation talent
Credit/ Default Risk
Risk Description
Default or any other failure to fulfil their current or future obligation by an obligor (e.g. debtor, client, tenant) with which the company conducts business
Risk Trend
Mitigation Measures
- Perform comprehensive credit assessments and background checks on clients, subcontractors, and suppliers before engagement
- Impose limits or require deposit or retention money from counterparties and maintain a diversified client portfolio to mitigate risk
- Continuously monitor receivables and generate regular reports to flag overdue balances for recovery actions
- Implement robust debt collection procedures and use technology to automate alerts and reminders for overdue payments
- Ensure compliance with credit control procedures and maintain regular communication with clients
Climate Risk
Risk Description
The risk of adverse impacts arising from climate change, including physical risks from natural disasters and extreme weather events, and transition risks associated with the shift to a low-carbon economy
Associated ESG Issue:
Climate Change
Risk Trend
Mitigation Measures
- Conduct climate scenario analysis to evaluate the financial impact of climate-related risk to provide insight for prioritization and formulation of climate adaptation strategies
Physical Risk - Establish necessary procedures including business continuity and recovery plans to respond to various natural disasters supported by regular drill exercises and training
- Leverage on technology to strengthen inspection and perform enhancement work on physical assets and facilities that are vulnerable to natural disaster and extreme weather
- Implement safety measures for heat stress and reduce outdoor work by advanced building methods
- Assess and ensure adequate insurance coverage to minimize potential financial loss
Transition Risk - Closely monitor and track climate-related regulatory and disclosure developments
- Integrate responsible investment requirements into the investment policy, including sectors exclusions and ESG due diligence with climate-related risk considerations
- Periodically review and update climate transition plans and implementation roadmaps
- Implement energy management and carbon monitoring initiatives, and explore and adopt cost-efficient low-carbon technologies, products and materials
The Board provides overall oversight of the Group’s ESG and sustainability matters and is ultimately accountable for the Group’s ESG strategy and progress against its goals and targets. With the delegation from the Board, the Audit Committee oversees risks, including ESG and climate-related risks, and evaluates the effectiveness of mitigation measures to manage the risks.
The Group applies its ERM process to assess, manage, monitor, and report ESG and climate-related risks. ESG risk profiles (including climate-related risks) and integration initiatives are reported regularly to the ERM Steering Group, Executive Committee, Audit Committee, and ESG Committee.
| Risk Identi fication | Material ESG issues, together with climate-related physical and transition risks, are integrated into the CTFS Risk Bank to support the systematic identification, assessment and management of ESG-related risks, in alignment with the strategic focus of the Group’s ESG priorities. The GRM team works closely with the Group ESG team to incorporate ESG insights into the risk identification process and engages with risk owners to assess and discuss relevant ESG risk factors. |
| Risk Assessment | The Group is committed to minimizing its negative impacts on the environment and society. It has integrated ESG considerations into its risk assessment process:
|
| Risk Treatment & Monitoring | Consistent with the Group’s ERM approach, KRIs and risk mitigation measures are developed for ESG-related risks by respective business units and corporate of fice departments, based on the nature and priorities of the identi fied risks and their associated ESG issues. To further strengthen climate risk oversight, the Group leverages climate scenario analyses to identify meaningful indicators that support the monitoring of key climate risk drivers and enable timely mitigation actions. The GRM team works closely with the Group ESG team, sharing ESG risk insights to support the effective management of ESG-related risks and the development of ESG initiatives. |
| Risk Awareness Building | Periodic training sessions are conducted to share our approach to managing ESG-related risks, as well as information and knowledge about emerging trends and popular ESG and climate-related topics to our management, risk owners and relevant individuals. ESG and climate considerations have also been incorporated in our regular risk induction training and deep-dive workshop on risk assessment. We also actively engage the Group ESG team and external experts to share their insights and best practices on management of ESG-related risks. All relevant training materials, together with the Group’s policies, procedures and guidance materials related to risk management and internal control, are centralized within the “ERM Library” module under ERMApps, the Group’s policies unifi ed digital ERM platform, to enhance the accessibility, consistent understanding and sharing of risk management knowledge, requirements and practices across the Group. |
| BCM Governance | Establishes a governance framework, together with clear roles, responsibilities and oversight mechanisms, to support effective BCM implementation across the Group |
| Group BCM Framework | Defines the principles, standards and requirements governing the development, implementation and ongoing maintenance of BCM capabilities and planning across the Group |
| Crisis Communication Plan | Provides a structured mechanism across the Group for timely crisis reporting, activation of the crisis management team, and appropriate communication with key stakeholders during crisis and disruption events |
| BCM Approach and Methodology | Incorporates Business Impact Analysis and Disruption Risk Assessment methodologies to identify critical business activities, assess disruption risks and evaluate business continuity preparedness, with a strong emphasis on regular training, testing, drills and reviews |
| Group Audit Reports |
|
| Whistleblowing Reports (if any) |
|
| Group Risk Management Reports |
|
| Review of Risk Management and Internal Control Systems |
|
| Management Confirmation through Integrated Internal Control Self-Assessment |
|
| External Auditor Reports |
|
Regarding the results of the review of the effectiveness of the risk management and internal control systems, please refer to the Corporate Governance Report in our annual report for details.


